Beyond Basic Bots: How Advanced Behavioral Validation Shields Australian Websites from Sophisticated Attacks
Consider a hypothetical scenario: an Australian fashion retailer’s Black Friday pre-sale landing page starts returning 500 errors in the early hours of the morning. No warning, no ransom note, no obvious DDoS flood. Just a slow, methodical creep of traffic that looks human enough to pass every basic firewall rule. Then the checkout database buckles under a wave of fake cart sessions in a matter of hours. This isn’t a script kiddie with a botnet. It’s a coordinated scraping and inventory-hoarding operation using residential proxies to mimic real shoppers, and it threatens to cost the business its biggest sales day of the year.
That’s the reality of running a website right now. The bots attacking Australian businesses don’t announce themselves anymore. They browse like customers, solve CAPTCHAs, rotate IP addresses across residential networks, and wait patiently between requests to dodge rate limits. Basic bot blocking, the kind built into most shared hosting and free-tier security plugins, simply can’t see them coming. Here’s why advanced bot management has become non-negotiable infrastructure, not an optional upgrade, for any business serious about protecting online operations in Australia.
What Is Advanced Bot Management?
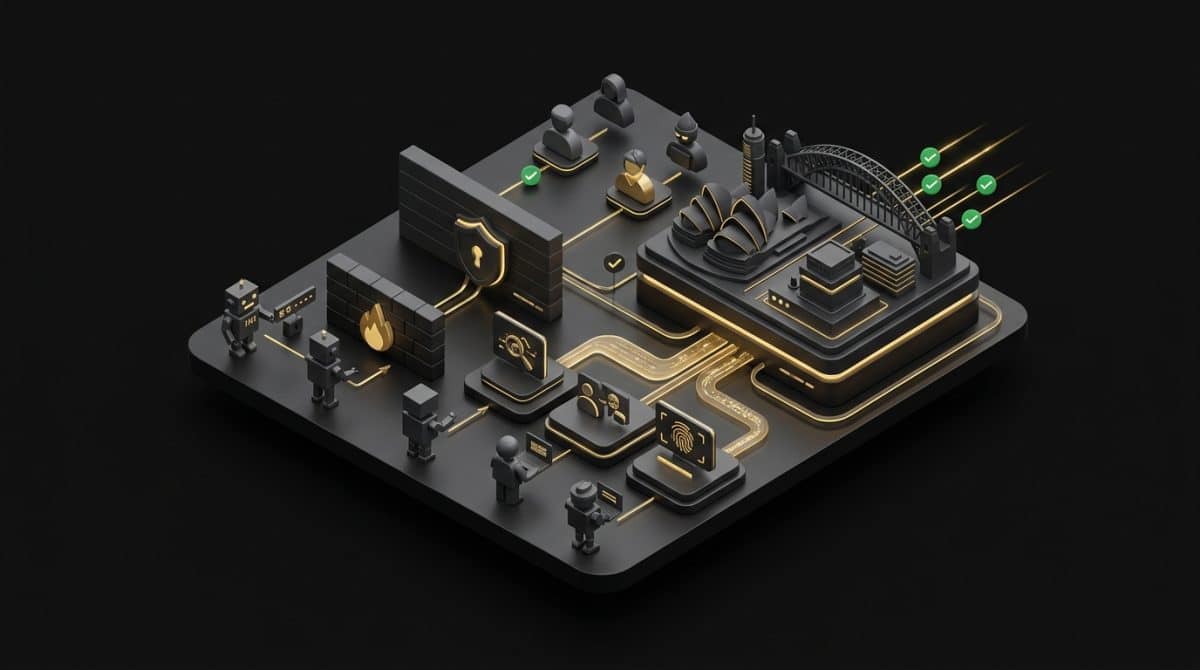
Advanced bot management analyses behavioural patterns, request fingerprints, and interaction signals in real time to separate genuine human visitors from automated traffic, even when that traffic is built specifically to look human. Basic bot filters lean on static IP blocklists or simple rate limiting. Advanced systems build a behavioural profile of every visitor and score it continuously throughout the session.
The shift matters because the threat landscape has changed fast. According to Cloudflare, automated bot traffic makes up a substantial and growing share of all internet requests, with an increasing proportion classified as sophisticated automated traffic engineered specifically to evade detection. These aren’t old-school scrapers hammering a server with obvious repetition. They mimic human-like interaction patterns, randomise timing between clicks, and rotate through residential IP addresses so no single address ever trips a threshold. For Australian businesses running WordPress, WooCommerce, or custom applications, the security model you had five years ago just doesn’t cut it anymore.
How Do Bots Bypass Basic Security?
Sophisticated bots bypass basic security by exploiting the narrow, static rules most firewalls rely on, rules that only catch obvious, high-volume, or previously-flagged threats. If a bot never repeats a pattern the firewall recognises, it sails through untouched.
Here’s how that plays out across three common attack types:
- Credential stuffing: Attackers run lists of leaked username and password combinations against your WordPress login (
wp-login.php) or WooCommerce customer accounts. Basic rate limiting catches rapid-fire attempts from one IP, so the attacker just spreads the attempts across thousands of different residential IPs. One attempt each. Nothing trips the alarm. - Inventory and price scraping is a different problem entirely. Competitors or scalper bots scrape product pages and pricing at scale, often disguising themselves as legitimate browsers with full user-agent strings and referrer headers. Basic security sees “normal” browser traffic and waves it through, even as it strips your competitive pricing data or hoards limited stock in abandoned carts.
- Then there’s Layer 7 DDoS. Rather than flooding your server with obvious junk traffic, attackers send genuine-looking HTTP requests to expensive endpoints, search functions or checkout pages, at a volume calculated to exhaust server resources without ever looking like a traditional flood. This is one of the trickiest forms of DDoS protection Australia businesses need to plan for, because it targets application logic, not just bandwidth.
The retailer in our opening scenario would have been hit by exactly that second category. The bots weren’t breaking anything. They were behaving just plausibly enough to slip past a standard WAF while quietly destroying the site’s performance and inventory accuracy.
What Does Behavioural Validation Look Like?
Genuine behavioural validation scores a wide range of signals per request, including interaction patterns, TLS fingerprints, header consistency, and historical reputation, then makes a real-time decision to allow, challenge, or block traffic before it ever reaches your application. Some platforms also assess finer-grained interaction signals such as mouse movement or typing cadence, though the precise mix of signals and their reliability varies by vendor and should be treated as one input among many rather than a silver bullet.
That’s fundamentally different from a static rule that says “block this IP” or “block this user agent.” A properly configured behavioural system keeps asking questions:
- Does this visitor’s browser fingerprint match the headers it’s presenting?
- Is the request timing consistent with human browsing, or suspiciously uniform?
- Has this IP range, ASN, or device fingerprint shown up associated with automated abuse anywhere else in the network?
- Is the visitor interacting with page elements the way a real person would, or just hitting the checkout API directly?
At Black Label Hosting, this is built into how we architect security for every client on our managed hosting plans. Not bolted on as an afterthought. Paired with server-level hardening and managed WordPress security practices, this behavioural layer catches the traffic plugin-based solutions were never designed to see.
How Do You Implement Advanced Bot Management?
Implementing advanced bot management means layering network-level filtering, application-level monitoring, and ongoing tuning. One plugin or firewall rule won’t do it. Here’s the practical sequence we run with clients:
- Audit current traffic for baseline behaviour. Before you can spot abnormal patterns, you need a solid stretch of clean traffic data showing normal visitor flow, average session length, and typical conversion paths.
- Deploy network-edge filtering. Route traffic through a layer that inspects requests before they hit your origin server, filtering by reputation, ASN, and known attack signatures. Most DDoS protection Australia providers start here, but it should never be the only layer.
- Add behavioural scoring at the application layer. Session consistency and interaction patterns get analysed here. Suspicious sessions are challenged with invisible checks rather than intrusive CAPTCHAs that hurt genuine customer experience.
- Harden login and checkout endpoints specifically. These are your highest-value targets. Enforce rate limits, watch for credential stuffing patterns, and lock down XML-RPC and REST API endpoints that aren’t in active use.
- Monitor and tune continuously. Bot behaviour evolves constantly. A configuration set once and forgotten will be obsolete within months. This needs to sit inside your ongoing managed hosting relationship, not a one-off security audit.
For agencies managing dozens of client sites, this model needs to scale without multiplying manual work. That’s exactly why managed hosting for agencies exists as a category. You shouldn’t be manually tuning bot rules across 40 different WordPress installs.
Why Do WordPress Sites Need Specialised Protection?
WordPress and WooCommerce sites need specialised bot protection because their popularity makes them among the most targeted CMS platforms in the world, and their plugin ecosystems introduce attack surfaces generic security tools simply don’t account for. WordPress powers a large majority of content-managed websites globally, according to WordPress.org. That scale means attackers build automated tools specifically designed to exploit its known weak points: wp-login.php, xmlrpc.php, outdated plugins, and exposed REST API routes.
A generic bot management tool built for “websites in general” won’t understand that a spike in requests to /wp-json/wc/store/cart is a WooCommerce-specific red flag for cart abandonment abuse or inventory scraping. Managed WordPress security has to understand the platform’s specific architecture, not just its HTTP traffic.
This matters even more for eCommerce operators. A WooCommerce store hit by scraper bots doesn’t just take a performance hit. It can lose pricing intelligence to competitors, have stock artificially reserved by fake carts, and watch genuine customers abandon slow-loading checkout pages. For stores running serious transaction volume, this level of protection needs to be paired with infrastructure that can actually handle the load once malicious traffic is filtered out. That’s why we built Business Class Hosting around this exact combination of security and performance.
What Happens When Bots Overwhelm Server Resources?
When bot traffic overwhelms server resources, legitimate customers get slow page loads, failed checkouts, and timeout errors, directly costing revenue even if no data is ever stolen. This is the part most businesses underestimate: you don’t need to be “hacked” to be seriously damaged by bots.
In our hypothetical retailer scenario, the business would stand to lose a significant share of sales during their pre-sale window without a single record ever being breached. Genuine customers simply couldn’t complete checkout while the server strained under fake sessions. After implementing behavioural bot filtering combined with a resource upgrade, a business in this position would typically see its next major sale event run without downtime despite a large increase in legitimate traffic, because the bot traffic never reached the application layer at all.
For high-traffic events, a sale, a product launch, a viral marketing campaign, server headroom matters just as much as the filtering itself. Blocking bots only helps if your infrastructure can also handle the legitimate surge that follows. This is where First Class Hosting and Managed VPS Hosting become relevant for businesses whose traffic patterns are unpredictable or seasonal.
What to Do Next
If you’re running a WordPress or WooCommerce site handling customer data, payments, or any meaningful traffic volume, basic security plugins aren’t enough anymore. Here’s where to start:
- Review your current hosting’s bot management capability. If it’s limited to a WAF plugin and IP blocklists, you’ve got a gap.
- Check your login and checkout endpoints specifically for rate limiting and behavioural monitoring, not just general firewall rules.
- Managing multiple client sites? Work out whether your current setup can scale bot management without manual per-site tuning.
- Get an infrastructure assessment before your next high-traffic event, not after it causes damage.
Bot traffic isn’t going away, and it isn’t getting less sophisticated. The businesses that hold up under pressure, whether that’s a Black Friday sale, a product launch, or an unexpected traffic spike, are the ones that treat advanced bot management as core infrastructure rather than an add-on plugin. Black Label Hosting builds advanced bot management directly into every managed hosting plan, paired with the server capacity to handle genuine traffic surges once the noise is filtered out. If you’re ready to find out where your current setup falls short, get in touch with our team for an infrastructure assessment before your next high-traffic event puts it to the test.